Platform · Data Privacy Gateway
Run cloud AI on real clinical data. Without the PHI ever leaving the building.
An on-premises tokenisation appliance for health systems. Cloud AI gets complete clinical data. Patient identities stay inside your firewall.
FHIR R4 native · mTLS re-identification, you hold the key
Tokenised before it crosses the firewall
Complete clinical data in the cloud. Zero identities.
The problem
The barrier was never the model.
Once PHI leaves the building for a cloud model, it is a breach surface, a BAA liability, and a sub-processor risk. So AI projects stall in legal review, and staff paste patient details into consumer chatbots anyway. The barrier is the identity attached to the record.
What DPG does
DPG removes the trade-off.
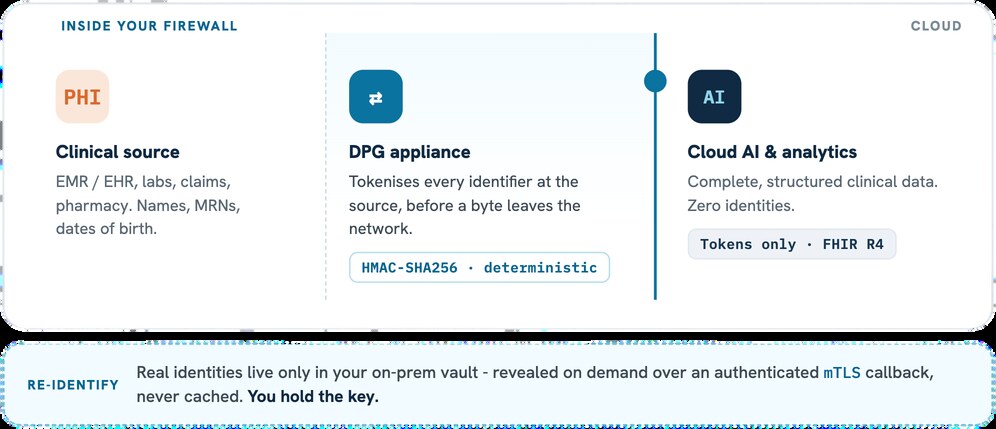
It tokenises every identifier at the source, before any data leaves your network. The cloud sees complete, structured clinical data, never a name, an MRN, or a date of birth.
- HMAC-SHA256, deterministic tokens
- Real identities stay in your on-prem vault
- Revealed only over authenticated mTLS
The cloud cannot leak PHI it never receives.
How DPG compares
Four approaches, compared.
| Hosted privacy vault Skyflow-type | Linkage network Datavant-type | LLM redaction Prompt proxy | IASORA DPG | |
|---|---|---|---|---|
| Where PHI lives | In the vendor's hosted vault | Tokenised for movement across a network | Passes through a gateway | Inside your building |
| Primary job | Isolate PII for app workflows | Link datasets for research and RWD | Filter prompts at the gateway | Tokenise full clinical data at source for cloud AI |
| FHIR native | Horizontal, not FHIR-led | Identifier-focused | No | R4 native |
| Utility after privacy | High, but vendor-held | Linkage only | Lossy redaction | Full structured clinical data, deterministic tokens |
| Re-identification | Vendor-mediated | Bilateral token transform | Not applicable | mTLS callback to your appliance, you hold the key |
Why it's different
Privacy as architecture, not a promise.
Tokenised at your firewall
Identities are tokenised before they cross your firewall, so the cloud never holds them.
Tokenised data stays useful
The same patient gets the same token everywhere, so longitudinal records, analytics, and linking still work.
Built for the security team
mTLS on every resolution call. Full audit trail. A pluggable encrypted vault you own.
The AI angle
Put cloud AI to work on real data.
Run cloud AI on real data
Complete clinical context, never an identity.
End shadow AI
Give clinicians a sanctioned path so they stop pasting PHI into consumer tools.
Deploy in weeks
A product that keeps identity behind the firewall.
De-identify by design
Analyse everything. Resolve only when authorised.
DPG is your on-ramp to IASORA: cloud-scale clinical analytics, AI, and interoperability, with privacy you can prove.